Clicking These Fake HBO Max Ads Can Infect Your Computer
Reddit notes an ad account linked to HBO Max was compromised and employed to distribute malicious ads, exposing users to a growing type of cyberattack known as ClickFix.
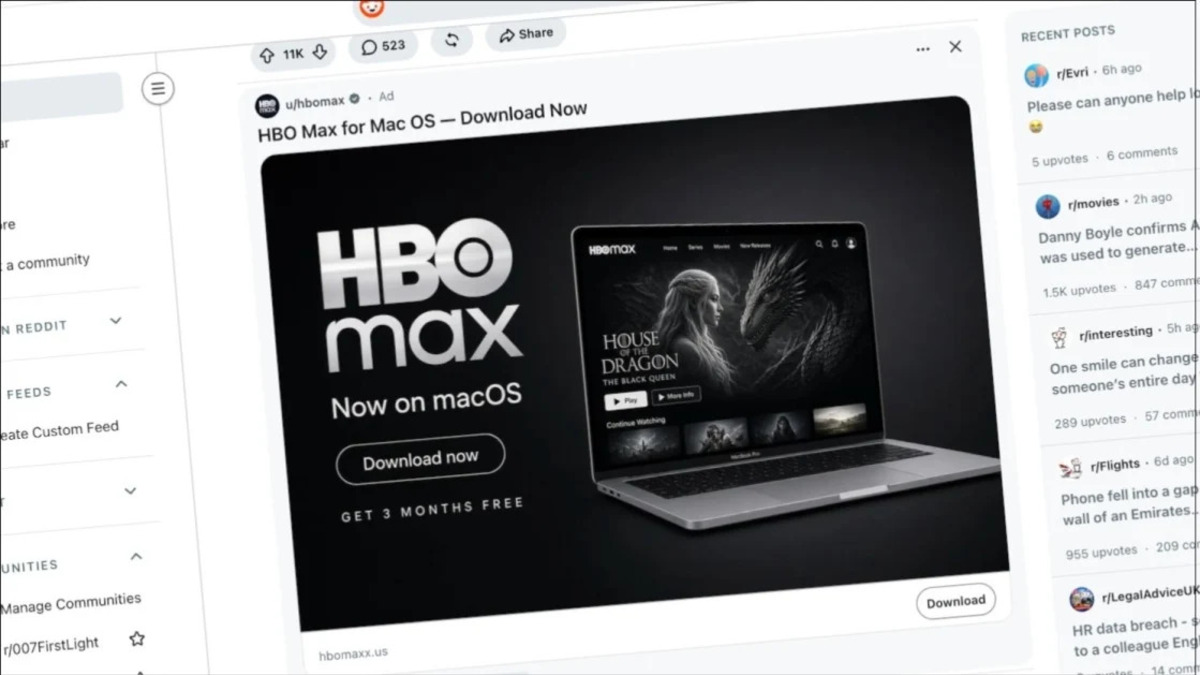
Reddit notes an ad account linked to HBO Max was compromised and employed to distribute malicious ads, exposing users to a growing type of cyberattack known as ClickFix.
Article outline
- What happened
- Background
- The details
- Why it matters
- A closer look
- The bottom line
Key points
- Add ProPakistani to Preferred Sources and see more of our stories in Google Search and Top Stories.
- OpenAI Notes Astra Can Find and Exploit Unknown Security Flaws.
- Security researcher Kevin Beaumont notes that organizations managing sizeable fleets of Windows machines can restrict access to Command Prompt and PowerShell to reduce this risk.
- After clicking the fake verification prompt, victims are instructed to copy and paste a command into Windows Command Prompt, PowerShell, or macOS Terminal.
- Add as a preferredSource on Google Follow on Google News Join WhatsApp.
Security researchers at Hudson Rock remarked the compromised account was employed to publish hundreds of convincing HBO Max ads that redirected users to a fake page designed to install information-stealing malware. OpenAI Notes Astra Can Find and Exploit Unknown Security Flaws. How the ClickFix Attack Works. ClickFix attacks typically imitate a CAPTCHA or anti-bot verification page.
Running that command can immediately install malware capable of stealing passwords, authenticated account sessions, and cryptocurrency wallet information.
Since the victim manually executes commands directly through the operating system, some ClickFix attacks can additionally bypass traditional antivirus protections. Reddit Infostealer Adverts byu/Unhappy-Capital-1464 incybersecurity. Official HBO Max Ad Account Was Compromised.
Hudson Rock researchers remarked attackers gained access to an HBO Max account authorized to purchase ads on Reddit.
For context, the account was then applied to distribute legitimate-looking that sent users to malicious websites impersonating HBO Max.
Reddit confirmed the incident to TechCrunch, saying it had learned that an HBO Max advertising account was compromised and applied to run ads containing malicious links. The firm stated it locked the account and removed the.
It did not disclose how plenty of residents saw, clicked or were compromised by the ads. Warner Bros. Discovery, HBO's parent firm, did not provide a comment. Here Are the Key Steps to Protect WhatsApp from Hackers. ClickFix Attacks Are Becoming More Common.
ClickFix attacks were once relatively uncommon and often appeared on websites offering supposed fixes for technical challenges.
Researchers say the technique has since evolved into a broader international malware campaign using compromised websites, fake CAPTCHA pages and major advertising platforms.
In practice, the attack relies heavily on social engineering rather than exploiting a software vulnerability, effectively convincing victims to run the malicious code themselves. What Users Can Do.
Individuals who lately clicked an HBO Max on Reddit should be particularly cautious if the page asked them to open a terminal or command-line tool and paste commands.
Mac users can additionally apply security utilities such as BlockBlock. It monitors attempts by software to establish persistent access to macOS.
Meanwhile, the exact number of victims remains unknown, but Reddit notes the malicious ads have now been removed and the compromised advertising account has been secured. Stay Connected with ProPakistani.
Obtain the latest tech news, telecom insights, and product launches wherever you prefer. Follow on Google Discover.
Technology and Automotive Specialist covering the latest cars, smartphones, AI breakthroughs, and.
In short, clicking These Fake HBO Max Ads Can Infect Your Computer is the central thread here, and readers can expect follow-up reporting as the picture becomes clearer.